Play all
Reverse engineering
344 videos • 191 hr 36 min
Part of Security. Ordered by how many people recommended each video and for how long; 19 are classics.
1 2 Compiling C to printable x86, to make an executable research paper
suckerpinch
Recommended by 10 •
Classic3 Break Me00 The MoVfuscator Turning mov into a soul crushing RE nightmare Christopher Domas
Adrian Crenshaw
Recommended by 7 •
Classic4 4 2 1 Christopher Domas The future of RE Dynamic Binary Visualization
Adrian Crenshaw
Recommended by 8 •
Classic5 27C3: Adventures in analyzing Stuxnet (Bruce Dang from Microsoft)
basti0007
Recommended by 8 •
Classic6 7 8 9 How I Fixed a 10 Year Old Guitar Hero Bug Without the Source Code
ExileLord
Recommended by 4 •
Classic10 11 12 [HOPE X] Elevator Hacking: From the Pit to the Penthouse
themarimbaincident
Recommended by 4 •
Classic13 DEF CON 23 - Chris Domas - Repsych: Psychological Warfare in Reverse Engineering
DEFCONConference
Recommended by 5 •
Classic14 15 16 Reversing WannaCry Part 1 - Finding the killswitch and unpacking the malware in #Ghidra
stacksmashing
Recommended by 2 •
17 DEF CON 26 - Christopher Domas - GOD MODE UNLOCKED Hardware Backdoors in redacted x86
DEFCONConference
Recommended by 4 •
Classic18 RE//verse 2026: Hacking the Xbox One by Markus 'doom' Gaasedelen
REverse Conference
Recommended by 3 •
19 20 21 Bare-metal ARM firmware reverse engineering with Ghidra and SVD-Loader
stacksmashing
Recommended by 2 •
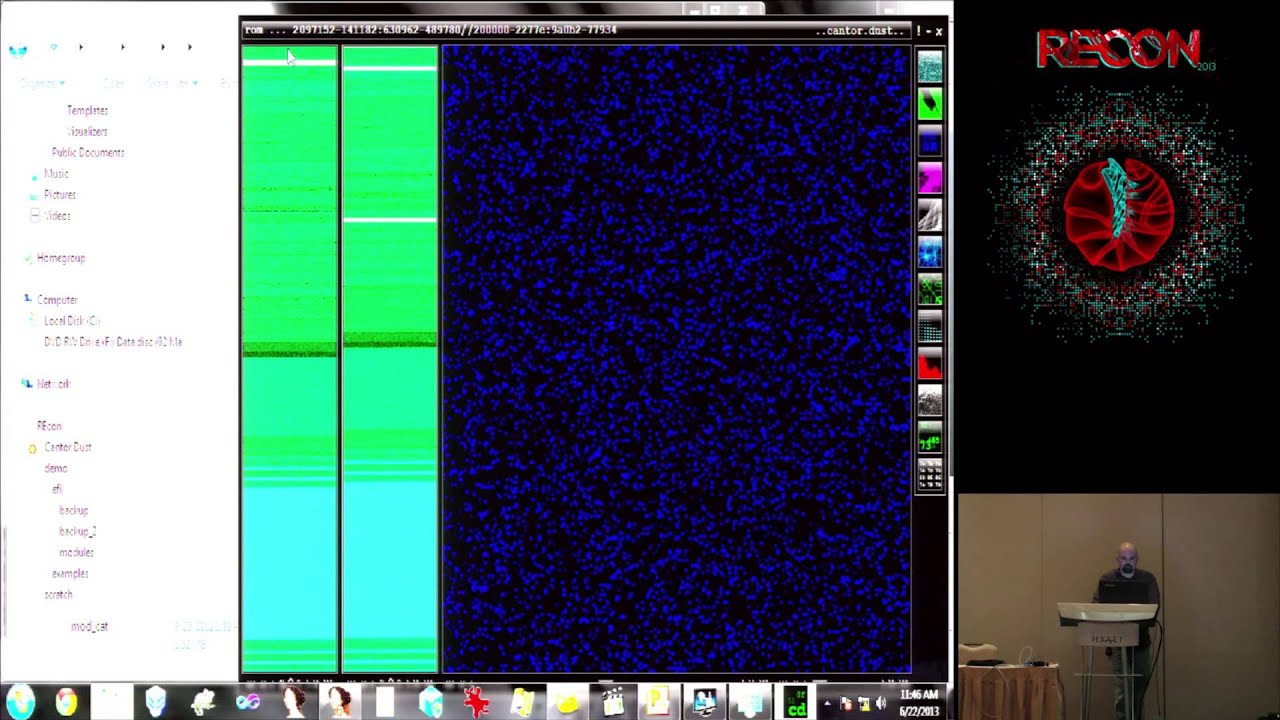
22 23 24 25 26 27 28 REcon 2013 - The Future of RE : Dynamic Binary Visualization (Christopher Domas)
Sébastien Duquette
Recommended by 3 •
Classic29 30 31 32 33 Finally Obtaining the Triforce in Ocarina of Time: Triforce Percent Explained
Retro Game Mechanics Explained
Recommended by 2 •
34 35 36 Alex Ionescu - The "Bird" That Killed Arbitrary Code Guard - Ekoparty 2017
Ekoparty Security Conference
Recommended by 2 •
Hidden gem37 38 39 DEFCON 17: Reverse Engineering By Crayon: Hypervisor Based Malware Analysis and Visualization
Christiaan008
Recommended by 2 •
Hidden gem40 REcon 2015 - Reversing the Nintendo 64 CIC (Mike Ryan, John McMaster, marshallh)
Sébastien Duquette
Recommended by 2 •
Hidden gem41 DEF CON 26 - Christopher Domas - The Ring 0 Facade Awakening the Processors Inner Demons
DEFCONConference
Recommended by 2 •
Classic42 39C3 - From Silicon to Darude Sand-storm: breaking famous synthesizer DSPs
media.ccc.de
Recommended by 2 •
43 44 45 Reverse engineering with #Ghidra: Breaking an embedded firmware encryption scheme
stacksmashing
Recommended by 1 •
46 47 48 49 Hardwear.io USA 2024: Breaking Into Chips By Reading The Datasheet - Mark Omo and James Rowley
hardwear.io
Recommended by 1 •
50 x64dbg and HxD Tutorial: How to Patch "CD Required" Errors (No-CD Patches) [PainKiller Editor]
Stephen Chapman
Recommended by 1 •
51 52 53 Pokemon Red/Blue Virus 2.0, and the Mew that was hiding under the truck all along.
MrCheeze
Recommended by 1 •
54 Let's Hack: Cuphead, Ep. 5 - No Player Collision [Cuphead Cheats via Cheat Engine]
Stephen Chapman
Recommended by 1 •
55 Cracking the C0dez: Reversing C++, Structs & Stack Frames with Ghidra - Full CrackMe Walkthrough
Nick Blundell
Recommended by 1 •
56 57 Reverse Engineering/Game Patching Tutorial: Full Res RollerCoaster Tycoon with Ghidra+x64dbg+Python
jeFF0Falltrades
Recommended by 1 •
58 59 Researcher Cracks Elder Scrolls Online, Dark Age of Camelot, and Wildstar (Livestream archive)
Motherboard
Recommended by 1 •
60 Why Are Emulators Legal? Dolphin vs. Nintendo, and the Fate of Emulation [Great Emu War Pt. 1]
Moon Channel
Recommended by 2 •
61 37C3 - Operation Triangulation: What You Get When Attack iPhones of Researchers
media.ccc.de
Recommended by 2 •
62 63 How to Crack and Patch Applications with Cheat Engine (Part 1) [LaFarge's CrackMe #2]
Stephen Chapman
Recommended by 1 •
64 65 Cracking a game like it is 1990 with the Amiga Action Replay [💉💉💉]
RetroLab
Recommended by 2 •
Hidden gem66 67 68 I hacked my old Mercedes instrument cluster to display custom text - Car infotainment project part 3
RAND_ASH
Recommended by 1 •
69 Cracking the C0dez: An Introduction to Ghidra Scripting and CPU Emulation - Full CrackMe Walkthrough
Nick Blundell
Recommended by 1 •
70 71 72 73 74 Getting Started Reversing C++ Objects with Ghidra - Ghidra Reversing Tutorials
Dr Josh Stroschein - The Cyber Yeti
Recommended by 1 •
75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 Understanding Pointers for Reverse Engineers - Pointer Basics in Assembly [ Patreon Unlocked ]
OALabs
Recommended by 1 •
94 Let's Hack: Extracting Firmware from Amazon Echo Dot and Recovering User Data
Matt Brown
Recommended by 1 •
95 GDB Tutorial for Reverse Engineers: Breakpoints, Modifying Memory and Printing its Contents
Path Cybersec [Slava Moskvin]
Recommended by 1 •
96 Malware Triage Tips: How To Stop Wasting Time in IDA On Packed Samples [ Twitch Clip ]
OALabs
Recommended by 1 •
97 Reverse Engineering 101: CPU, memory, debugging and cheating in minesweeper
Path Cybersec [Slava Moskvin]
Recommended by 1 •
98 Exploiting (and Patching) a Zero Day RCE Vulnerability in a Western Digital NAS
Flashback Team
Recommended by 1 •
99 100 101 102 Animal Crossing Has Been Decompiled! The Future of Retro Gaming
Video Game Esoterica
Recommended by 1 •
103 Cracking Konami M2 Encryption - Tech Deep End - Video Game Esoterica
Video Game Esoterica
Recommended by 1 •
104 Intro to Shellcode Analysis: Tools and Techniques
SANS Digital Forensics and Incident Response
Recommended by 1 •
105 Let's Hack: ELEX, Ep. 6 - Custom Health Regeneration! (CreateThread via Cheat Engine)
Stephen Chapman
Recommended by 1 •
106 107 108 109 110 Ghidra and IDA - Solving a reverse engineering CTF crackme - AmIRootYet - Pranshu Bajpai
Pranshu Bajpai
Recommended by 1 •
111 Unpacking Redaman Malware & Basics of Self-Injection Packers - ft. OALabs
LiveOverflow
Recommended by 1 •
112 "The Linux Kernel Hidden Inside Windows 10" techtalk by Alex Ionescu
ReactOS Community
Recommended by 2 •
113 114 Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
DarkMentorLLC
Recommended by 1 •
115 Recovering Meaningful Variable Names in Decompiled Code
Software Engineering Institute | Carnegie Mellon University
Recommended by 1 •
116 Reverse Engineering with Binary Ninja and gdb a key checking algorithm - TUMCTF 2016 Zwiebel part 1
LiveOverflow
Recommended by 1 •
117 118 119 Hack.lu 2017 Lightning Talk: RetDec: An Open-Source Machine-Code Decompiler by Peter Matula
Cooper
Recommended by 1 •
120 121 122 123 Using Logic Programming to Recover C++ Classes and Methods from Compiled Executables
Association for Computing Machinery (ACM)
Recommended by 1 •
124 IRC Botnet Reverse Engineering Part 1 - Preparing Binary for Analysis in IDA PRO
OALabs
Recommended by 1 •
125 Reversing in action: Golang malware used in the SolarWinds attack. Part 1
Kaspersky Tech
Recommended by 1 •
126 127 128 129 130 Ethereum/EVM Smart Contract Reverse Engineering & Disassembly - Blockchain Security #3
FuzzingLabs
Recommended by 1 •
131 132 133 134 Reverse Engineering/Bashing Splinter Cell to See What Falls Out | DitD Episode 1
jeFF0Falltrades
Recommended by 1 •
135 136 137 138 Can You Crack This Program? (Beginner Reverse Engineering Tutorial)
Dr. Pavel Vlašánek
Recommended by 1 •
139 140 141 142 143 144 SUNBURST SolarWinds Malware - Tools, Tactics and Methods to get you started with Reverse Engineering
cybercdh
Recommended by 1 •
145 146 147 How to Make a FlyCam from Scratch - Part 1: Coordinates, Rotation, and More!
Stephen Chapman
Recommended by 1 •
148 [Vulnerability Analysis] Binary diffing/Patch Diffing for beginners
Fuzzing_in - Hardik Shah
Recommended by 1 •
149 150 151 BSides Rochester 2023 Hardware Hacking:A Brief Primer on Reverse Engineering Bluetooth Transmissions
Actuator
Recommended by 1 •
152 153 154 155 Toorcon: San Diego (2014) - Cyber Necromancy: Reverse Engineering Dead Protocols
zi
Recommended by 1 •
156 Game Hacking Tutorial: Advanced Key-Press Tracing and Handling in Unity Games with Cheat Engine!
Stephen Chapman
Recommended by 1 •
157 Unpacking Pykspa Malware With Python and IDA Pro - Subscriber Request Part 1
OALabs
Recommended by 1 •
158 159 160 161 162 RedTeam Tricks Exposed - Reversing Engineering Syscalls To Evade Detection
OALabs
Recommended by 2 •
Hidden gem163 164 165 166 x86 In-Depth: CDECL Calling Convention Complete Tutorial - BONUS video
BinaryAdventure
Recommended by 1 •
167 168 169 170 171 172 Unpacking Gootkit Part 2 - Debugging Anti-Analysis Tricks With IDA Pro and x64dbg
OALabs
Recommended by 1 •
173 Breaking Obfuscated Binaries with AI Agents: An Attacker’s Playbook
Tim Blazytko
Recommended by 1 •
Recent pick174 175 Ilfak Guilfanov - Decompiler internals: Microcode [RootedCON 2018 - ENG]
Rooted CON
Recommended by 1 •
176 Chip-Off Firmware Extraction and Reverse Engineering of Arris SB6121 Cable Modem
Matt Brown
Recommended by 1 •
177 178 179 Unpacking Princess Locker and Fixing Corrupted PE Header (OALabs x MalwareAnalysisForHedgehogs)
OALabs
Recommended by 1 •
180 181 182 183 IoT Security: Backdooring a smart camera by creating a malicious firmware upgrade
stacksmashing
Recommended by 1 •
184 185 PyPANDA: Generic unpacking based on whole-system record and replay with Ghidra integration.
AdaLogics
Recommended by 1 •
186 Malware Analysis - Code Injection via CreateRemoteThread & WriteProcessMemory
MalwareAnalysisForHedgehogs
Recommended by 1 •
187 188 189 190 191 192 IDA Pro Scripting Intro - Automate Dynamic Import Resolving for REvil Ransomware
OALabs
Recommended by 1 •
193 194 Malware Theory - Packer identifiers don't tell you if a file is packed
MalwareAnalysisForHedgehogs
Recommended by 1 •
195 GNU poke: an extensible editor for structured binary data - GNU Tools Cauldron 2019
GNU Tools Cauldron
Recommended by 1 •
196 197 198 29C3: Many Tamagotchis Were Harmed in the Making of this Presentation (EN)
Christiaan008
Recommended by 1 •
199 200 IRC Botnet Reverse Engineering Part 2 - Analyzing Memory Structures with x64dbg and IDA PRO
OALabs
Recommended by 1 •
201 Reversing in action: Golang malware used in the SolarWinds attack. Part 2
Kaspersky Tech
Recommended by 1 •
202 Hardwear.io 2017: Reverse Engineering Of Programmable Logic Bitstreams by Andrew Zonenberg
hardwear.io
Recommended by 1 •
203 204 205 206 207 208 209 210 How I documented all CVar values in WoW 3.3.5.12340 - Function Hooking with C++ & MS Detours
DrFrugal
Recommended by 1 •
211 212 213 214 Malware Analysis - Unpack and Decompile PyInstaller Malware
MalwareAnalysisForHedgehogs
Recommended by 1 •
215 216 Reversing Engineering FlyHack Tutorial NoClip IDA pro Cheat Engine C++
Guided Hacking
Recommended by 1 •
217 218 219 220 Integrated Circuit Offensive Security | Olivier Thomas from Texplained | hardwear.io USA 2019
hardwear.io
Recommended by 1 •
221 222 Let's Hack: Terraria, Ep. 1 - .NET Hacking with Cheat Engine (Enumerate DLLs and Symbols)
Stephen Chapman
Recommended by 1 •
223 224 225 226 227 How does the Critical Hit with the Whip work in Castlevania? - Behind the Code
Displaced Gamers
Recommended by 1 •
228 229 230 231 The Bad Jump Design and 30 FPS Gravity of TMNT (NES) - Behind the Code
Displaced Gamers
Recommended by 1 •
232 233 234 235 236 Lunii - Fabrique à histoire : Réparation + Reverse engineering (1/2)
TBD électronique
Recommended by 1 •
237 238 Converting the Konami 3DO M2 to Run Different Games - Tech Deep End - Video Game Esoterica
Video Game Esoterica
Recommended by 1 •
239 240 241 242 Unpacking Modified UPX: DvdShrink Case Study (OEP Discovery & Manual Dump)
Kadir&Mira
Recommended by 1 •
243 244 245 Malware Analysis - Malware Hunting and Classification with YARA
MalwareAnalysisForHedgehogs
Recommended by 1 •
246 Karl Trygve Kalleberg - Frida: Putting the open back into closed software
OSDC Nordic
Recommended by 1 •
247 248 249 250 251 252 253 254 255 256 257 258 259 260 261 262 263 264 265 266 Ole André Vadla Ravnås - Frida: The engineering behind the reverse-engineering
OSDC Nordic
Recommended by 1 •
267 268 269 Reverse Engineering Sherlock Holmes Style: Obfuscated APIs & The Art of Deduction. - Katie
BSides Canberra
Recommended by 1 •
270 271 272 273 274 275 276 277 278 #days: Felix "FX" Lindner: Targeted Industrial Control System Attacks - Lessons from Stuxnet
DEFCON Switzerland
Recommended by 1 •
279 280 BSides DC 2018 - Lightning fast CTF solving - Automatic Exploit Generation & Side Channel Analysis
BSides DC
Recommended by 1 •
281 282 283 284 285 286 287 The Lamer Exterminator Amiga Virus - pt 1/2 - Behavior and Encryption [💉💉💉]
RetroLab
Recommended by 1 •
288 289 290 291 Learning with ReversingLabs: Identifying File Content with YARA Rules Whiteboard
ReversingLabs
Recommended by 1 •
292 Hardware Power Glitch Attack (Fault Injection) - rhme2 Fiesta (FI 100)
LiveOverflow
Recommended by 1 •
293 294 295 296 297 298 299 Reverse engineering Zhiyun Crane/Evo rage gimbal bluetooth commands
Press any key to continue…
Recommended by 1 •
300 301 302 303 304 305 306 "Program analysis for reverse engineers: from ⊤ to ⊥" - Adrian Herrera
BSides Canberra
Recommended by 1 •
307 OffensiveCon19 - Alex Ionescu - Keynote - Reversing Without Reversing
OffensiveCon
Recommended by 2 •
Hidden gem308 309 310 How is this speedrun possible? The Legend of Zelda World Record Speedrun Explained
Bismuth
Recommended by 1 •
311 312 Elise Mansbridge: Breaking the black-box security coprocessor in the Nintendo Switch, a story of vul
media.ccc.de
Recommended by 1 •
313 314 315 316 DEF CON 25 - Ilja van Sprundel - Are all BSDs are created equally? A survey of BSD kerne
DEFCONConference
Recommended by 1 •
317 318 319 320 321 322 323 Program Synthesis in Reverse Engineering - Rolf Rolles at Fastly Security Speaker Series
Fastly
Recommended by 1 •
324 325 DEF CON 23 - Charlie Miller & Chris Valasek - Remote Exploitation of an Unaltered Passenger Vehicle
DEFCONConference
Recommended by 2 •
326 What Nobody Tells You About Becoming a Vulnerability Researcher
Guided Hacking
Recommended by 2 •
Hidden gem327 328 Resident Evil Village PC DRM: Cracked Code Really Does Run Better - Confirmed
Digital Foundry
Recommended by 1 •
329 DeepSec 2010: All your baseband are belong to us by Ralf Philipp Weinmann
Sicherheitsforschung
Recommended by 1 •
330 331 DEF CON 32 - From getting JTAG on the iPhone 15 to hacking Apple's USB-C Controller - Stacksmashing
DEFCONConference
Recommended by 1 •
332 DEF CON 33 - Unmasking the Snitch Puck: IoT surveillance tech in the school bathroom - Reynaldo, nyx
DEFCONConference
Top upload •
333 DEF CON 31 - Infinite Money Glitch - Hacking Transit Cards - Bertocchi, Campbell, Gibson, Harris
DEFCONConference
Top upload •
334 DEF CON 32 - Anyone can hack IoT- Beginner’s Guide to Hacking Your First IoT Device - Andrew Bellini
DEFCONConference
Top upload •
335 336 DEF CON 30 - stacksmashing - The Hitchhacker’s Guide to iPhone Lightning and JTAG Hacking
DEFCONConference
Top upload •
337 338 339 340 DEF CON 31 - Vacuum Robot Security & Privacy Prevent yr Robot from Sucking Your Data - Dennis Giese
DEFCONConference
Top upload •
341 342 343 DEF CON 31 - Warshopping- Phreaking Smart Shopping Cart Wheels Through RF Sniffing - Joseph Gabay
DEFCONConference
Top upload •
344 DEF CON 33 - Cash, Drugs, and Guns - Why Your Safes Aren't Safe - Mark Omo, James Rowley
DEFCONConference
Top upload •